
Your Board Asks About Cyber Risk.
You Don't Have an Answer Yet.
Strategic security leadership, fractional cost. From first assessment to board-ready programme in 90 days.
Aligned with leading frameworks
Service Lines
Frameworks
Days to Board-Ready
The Security Leadership Gap
Without a security strategy, risk and regulatory exposure grow unnoticed. Regulations won't wait for you to catch up.
No CISO, No Strategy
Board questions go unanswered. Risk accumulates silently. Compliance deadlines slip past unnoticed.
Full-Time Is Unaffordable
A full-time CISO is a senior executive hire that is costly and slow to recruit. That's budget better spent on growth.
Regulators Are Moving
NIS2 enforcement underway. DORA active since January 2025. Personal liability for directors.
From Zero to Board-Ready
A structured 90-day journey from first assessment to functioning security programme.
Assess
Discovery interviews, asset inventory, gap analysis across controls, policies, and regulatory obligations.
Stakeholder mapping · Threat landscape · Current-state report
Build
Governance framework, policy suite, risk register, control implementation, and compliance mapping.
Prioritised roadmap · Board-ready reporting · Quick wins delivered
Run
Ongoing fractional CISO leadership — quarterly business reviews, incident oversight, and regulatory watch.
Continuous improvement · Team mentorship · Audit preparation
Board-ready security programme in 90 days
Six Service Lines.
One Integrated Programme.
Each service stands alone or connects into a unified security programme tailored to your stage and sector.
Fractional & Virtual CISO
Most requestedGet an experienced CISO on your terms. From quarterly board reporting to hands-on security programme buildout, our fractional leaders integrate with your team and operate as a true extension of your executive bench.
Learn moreKey Deliverables
- Security strategy and roadmap
- Board and executive reporting
- Team mentoring and capability building
- Incident response leadership
Built for Your Industry
Right-sized security leadership for organisations at every stage.
Series A–C · 50–500 employees
Enterprise customers demand SOC 2 reports before signing. Investors want security maturity before funding. Your IT team handles operations but nobody owns the security strategy — and every sales cycle is another security questionnaire you're scrambling to complete.
Not sure which engagement fits? Let's find out together
We Track the Rules So You Don't Have To
Real-time regulatory monitoring across EU, UK, and international jurisdictions.
61+ Frameworks. One Unified View.
Every engagement draws on deep framework expertise — mapped, cross-referenced, and continuously updated.
Advisory Backed by Platform
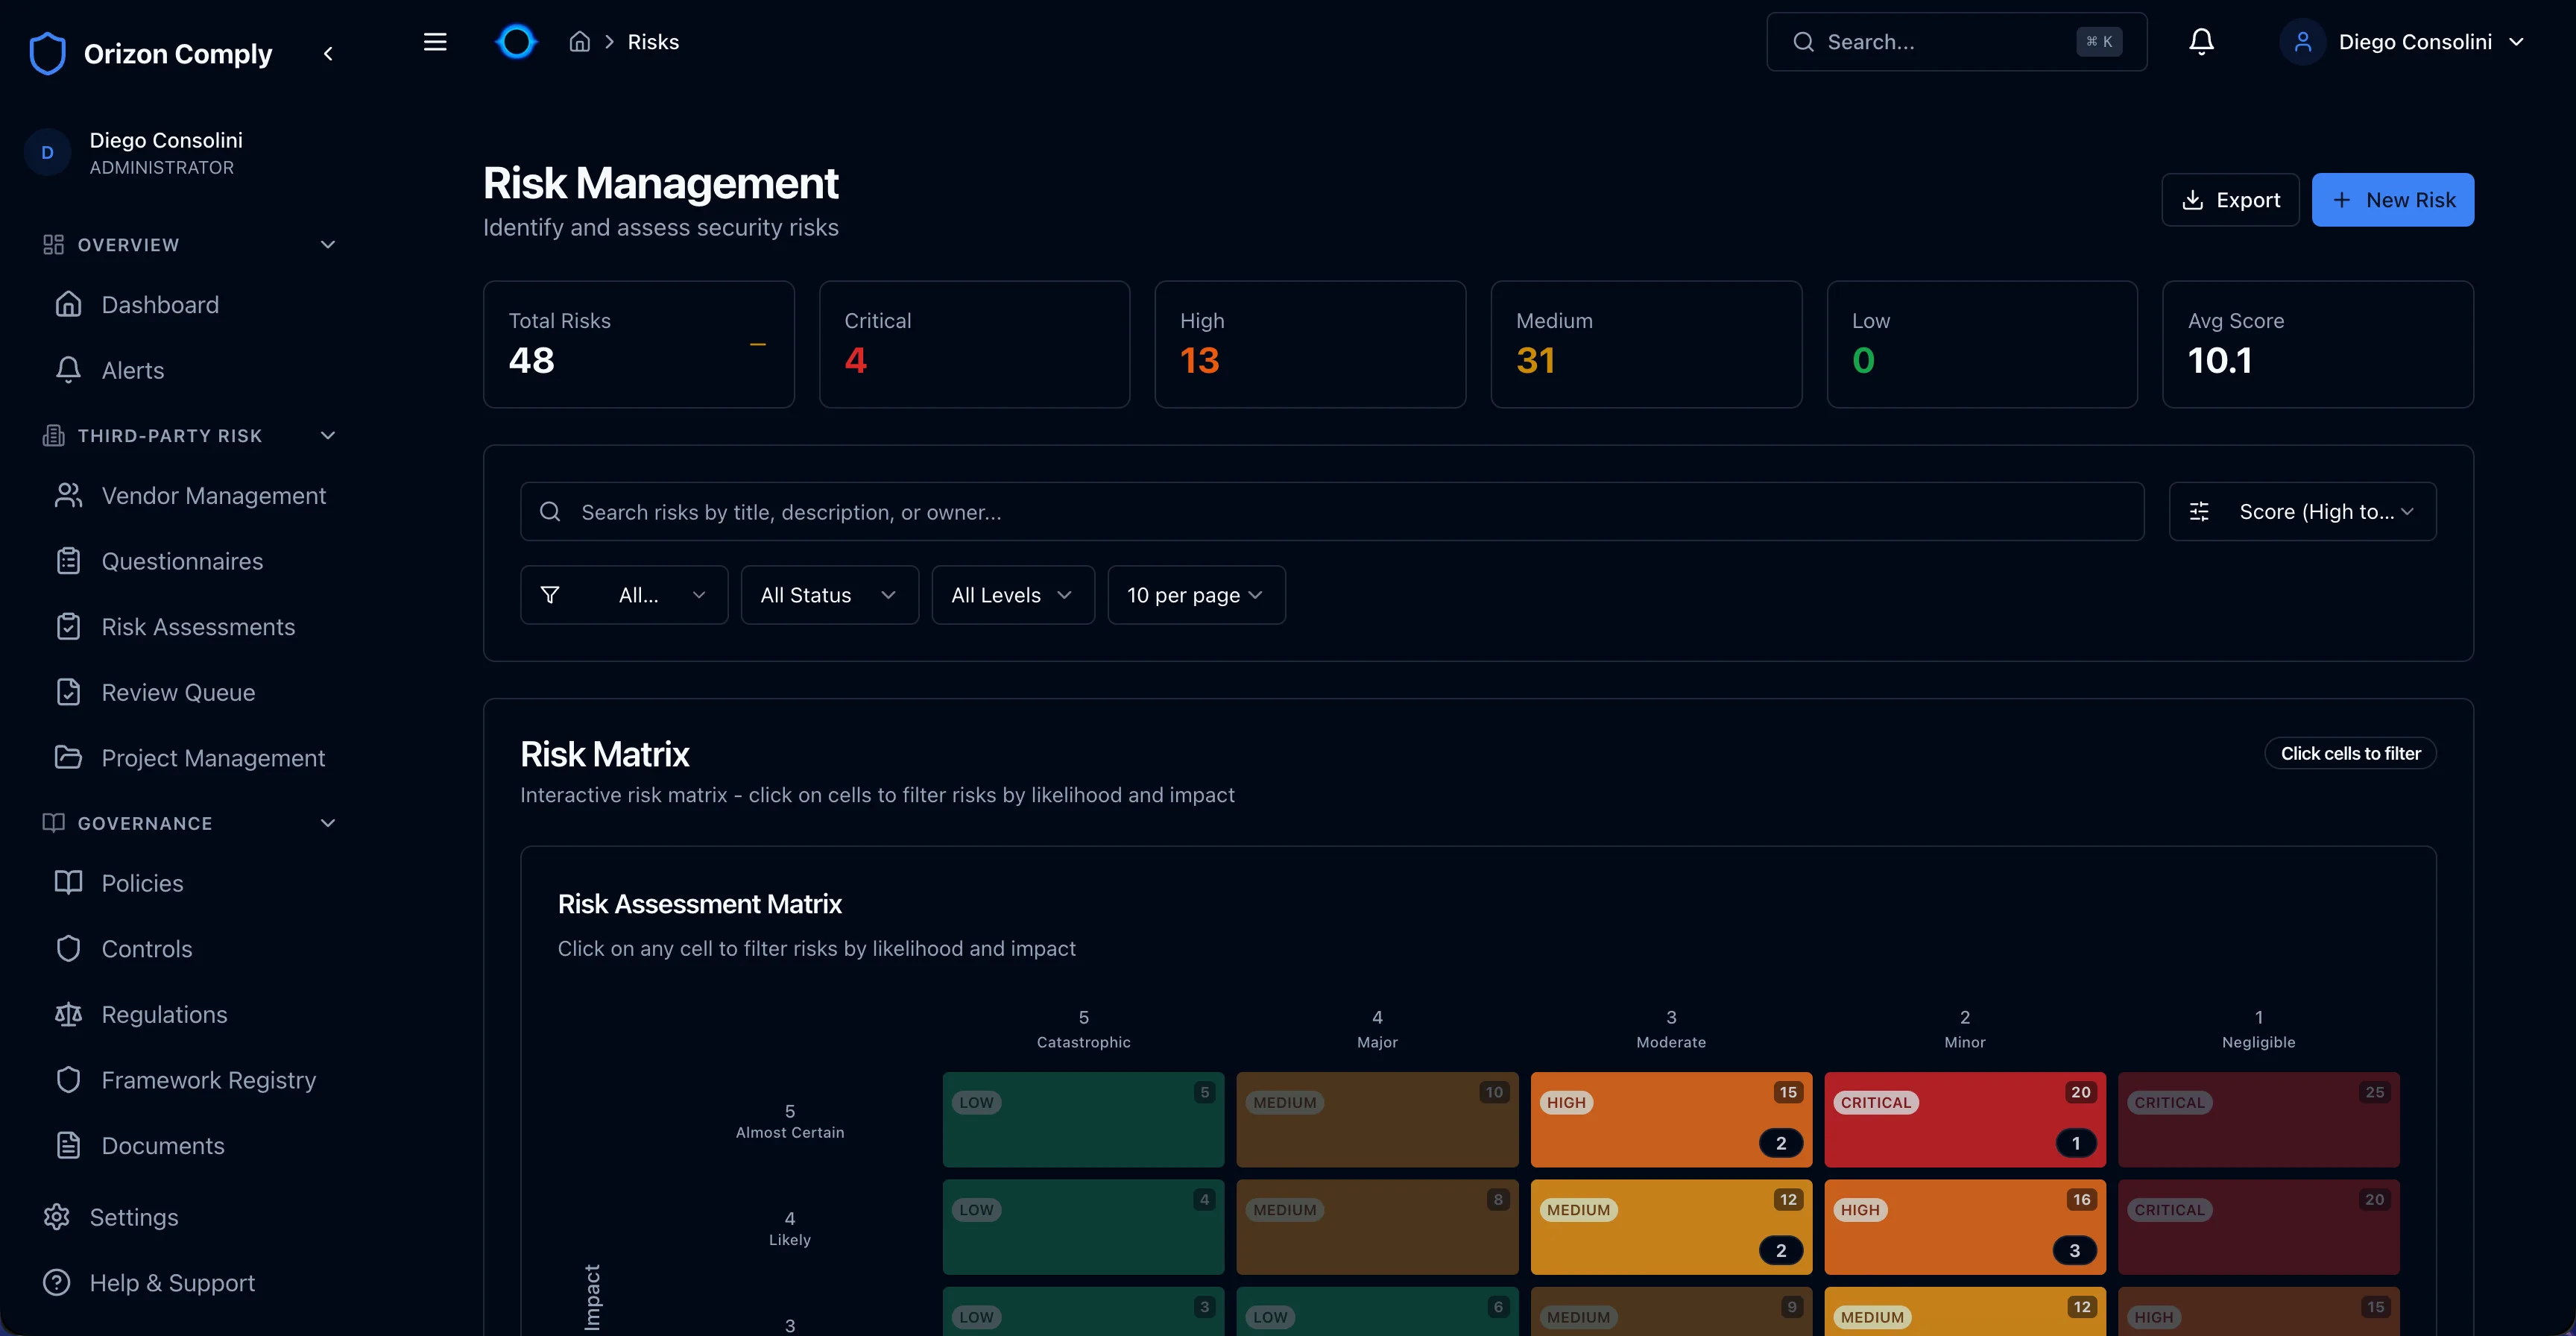
Unlike pure consulting, every engagement is powered by our GRC platform — automating evidence collection, mapping controls across frameworks, and generating board-ready reports in real time.
Frameworks
Controls
AI Agents
Orizon Comply — GRC platform with regulation tracking and AI audit
PolicyForge — AI-powered policy management
FrameworkMapper — OT/ICS compliance framework correlation
Outcomes That Matter
Measurable results from fractional security leadership.
To Board-Ready Programme
Integrated Service Lines
Frameworks Mapped
Controls Tracked
What Our Clients Say
We work under NDA with most clients. Want to hear from a reference? Ask us during your discovery call.
Ready to Close the Security Gap?
Book a free discovery call. We'll assess your current posture, identify immediate risks, and outline a 90-day roadmap — no commitment required.
Confidential · No obligation · Response within 24 hours